· ReadyStack
Worked example
Real numbers from this tool, line by line.
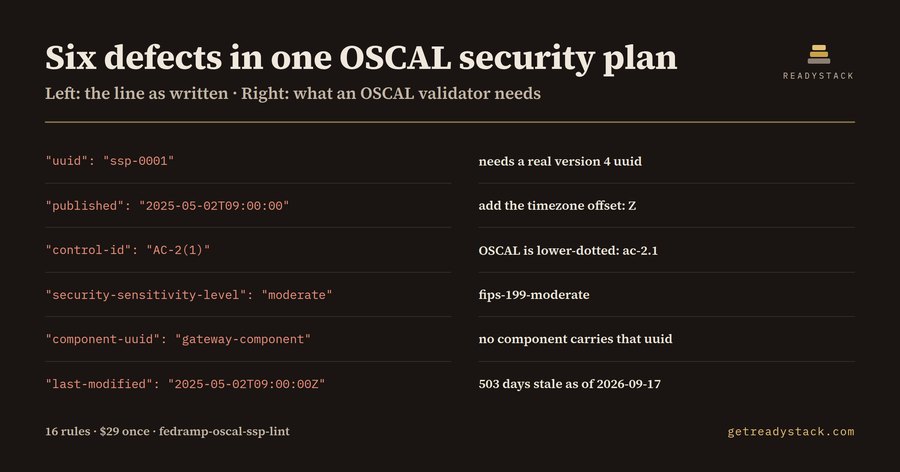
One FedRAMP Moderate system security plan, 19 findings across 14 checks, 12 of them high — and the compliance lead at the cloud vendor who owns it had seen none of them, because the first reader of an OSCAL package is never a person.
An OSCAL system security plan is JSON. Before an agency reviewer or a 3PAO assessor opens it, it passes a machine that knows the OSCAL datatypes, and that machine answers in JSON pointers. "Value at /system-security-plan/metadata/last-modified does not match pattern" is a true sentence and a useless one: it does not say what to write instead.
FedRAMP OSCAL SSP Lint is a VS Code extension and a single web page — same engine, same rule file — that runs 16 checks over a system-security-plan JSON and answers the other way round: here is the line, here is the replacement.
Four defects a generator reliably produces
Uuids that are not uuids. OSCAL's uuid datatype pins the version nibble: an RFC 4122 version 4 or 5 UUID, nothing else. Hand-written ids such as ssp-0001 or info-type-1 fail the pattern, and so does a tidy sequential id with a 1 where the 4 belongs.
Timestamps without a timezone. metadata.last-modified is a dateTime-with-timezone: 2026-09-17T09:00:00 is rejected, 2026-09-17T09:00:00-04:00 is accepted.
Control ids copied out of the catalogue. NIST writes AC-2(1); OSCAL writes ac-2.1 — lowercase, dot for the enhancement. Every narrative pasted from a Word matrix carries the wrong form.
References that point nowhere. A component-uuid, or an entry in party-uuids, has to resolve to a uuid defined in the same document. When it does not, nothing breaks loudly: the control simply claims to be implemented by a component the plan never defines.
Measured on the bundled sample
_fixtures/clean.json is a FedRAMP Moderate skeleton: one organization, two components, three implemented requirements, every datatype correct. It returns 0 findings.
_fixtures/dirty.json is the same plan after a generator and a copy-paste pass: 19 findings across 14 of the 16 checks — 12 high, 6 medium, 1 low. The root uuid is ssp-0001; published carries no offset; import-profile is missing; security-sensitivity-level reads moderate instead of fips-199-moderate; two of the three FIPS 199 objectives are absent; AC-2(1) sits where ac-2.1 belongs; a component-uuid names gateway-component; and ac-6 carries no implementation-status prop.
Two findings that move with the date
Two checks are clocks, which is why the page has an "as of" box.
metadata.last-modified on the sample is 2025-05-02T09:00:00Z. As of 2026-09-17 that is 503 days stale — continuous monitoring expects a yearly re-stamp. Check the same file as of 2027-01-15 and it reads 623 days.
Control cp-9 is planned with a planned-completion-date of 2026-06-30: 79 days overdue as of 2026-09-17, 199 days as of 2027-01-15. A planned control whose date has passed is a POA&M item that stopped being a plan.
Where the line is drawn
Free, no key, nothing uploaded: one system-security-plan JSON, all 16 checks, every finding with its JSON path, severity and fix. That job finishes — correct the file and ship it.
The licensed part is a different scope, not a crippled copy: it sweeps every OSCAL file in the workspace, resolves uuid references across the package rather than inside one file, and writes a dated report for a 3PAO. $29 once, one licence key per person or CI seat, 7-day full refund. Hand-review by a FedRAMP advisory consultant runs $150 to $300 an hour.
15 seconds — what it actually does
Questions people ask
What does FedRAMP OSCAL SSP Lint actually do?
It opens a system-security-plan JSON file and runs 16 checks against it: the five required OSCAL assemblies, metadata fields, RFC 4122 version 4 uuids, uuid references that must resolve inside the file, timezone offsets on last-modified, lower-dotted control ids such as ac-2.1, the FIPS 199 vocabulary, implementation-status props, and the 365-day continuous-monitoring clock. Each finding names a JSON path and the replacement text.
Who is this for?
Engineers and compliance leads at cloud service providers assembling a FedRAMP authorization package in OSCAL, and the 3PAO staff who read those packages. If you hand-write or generate system-security-plan JSON and the first thing that reads it is a validator rather than a person, this is aimed at you. It assumes no OSCAL tooling beyond a text editor.
Why is a free JSON schema validator not enough?
A schema validator answers with a pattern mismatch at a JSON pointer. It tells you that a string failed a regex, not that the uuid needs a version 4 nibble, nor which component the dangling component-uuid meant to name. It also has no opinion about a plan stamped 503 days ago, an overdue planned-completion-date, or the word TBD sitting in a narrative a reviewer reads.
What is free and what needs a licence key?
Free and offline: one system-security-plan JSON, all 16 checks, every finding with its JSON path, severity and the fix. That job is complete on its own. The licensed part is a different scope: it sweeps every OSCAL file in the workspace, resolves uuid references across files rather than within one, and writes a dated report to hand to your 3PAO.
What would this cost me otherwise?
Hand-review by a FedRAMP advisory consultant runs $150 to $300 an hour, and reading one package line by line is not a one-hour task. The alternative is free: submit, wait, and have the package returned with a schema path. The extension is $29 once, one licence key per person or CI seat,.
Why not just ask ChatGPT or another AI chat?
A general AI chat answers from training data with a cutoff date, cannot read your repository and names no rule version. FedRAMP OSCAL SSP Lint checks the file you open against 16 rules from a rule set dated 2026-09-20, and points at the exact line with the fix. For a filing, an audit or a client you need that dated result on your own files.
Ask about this tool
One question, answered by the person who built it. Your email only if you want the answer sent.